
Subscribe To Our Newsletter!
Subscribe to the newsletter to stay up to date with the latest news and most useful
Newsletter
↑
Back to Top



Product Overview |
|---|
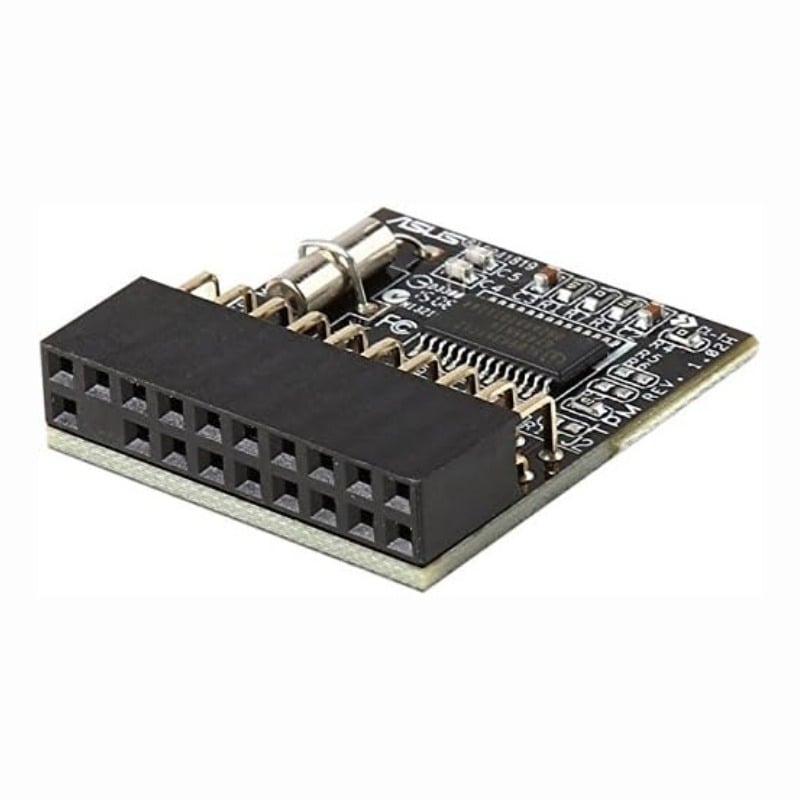
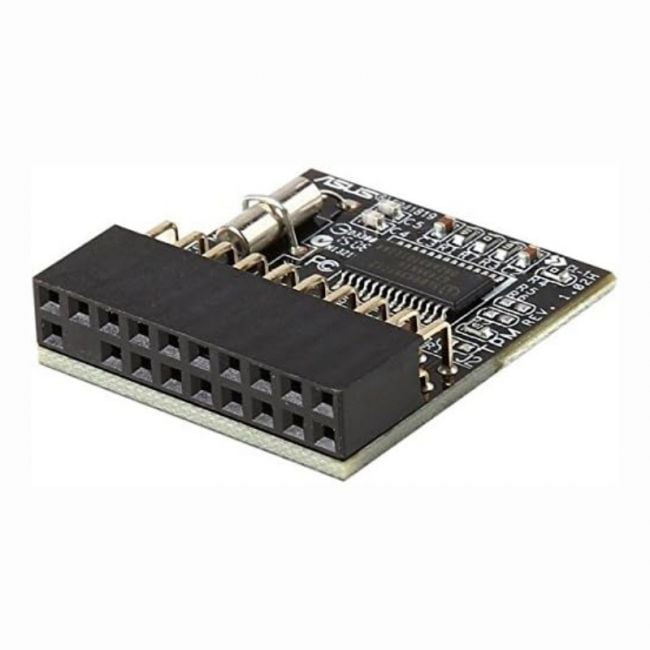
The TPM/FW3.19 Trusted Platform Module is a hardware security component designed to integrate with Asus motherboards. It provides robust cryptographic support and platform trust, playing a central role in protecting sensitive data and validating system integrity in various computing environments. |
General Information |
|
|---|---|
| Brand | ASUS |
| Part Number | TPM/FW3.19 |
Technical Information |
|
|---|---|
| tpm_interface | LPC |
| TPM Version | TPM 2.0 |
| Compatibility | ASUS system boards / motherboards with TPM header (supports ASUS TPM module) |
Miscellaneous |
|
|---|---|
| Assembly Required | Yes |
| Eco Friendly | Yes |
| Compliance Standards | WEEE, RoHS, cURus, CE, FCC, CCC, UL, TUV, cULus, CSA, cUL |
Physical Characteristics |
|
|---|---|
| Form Factor | Discrete module (header-mounted) |
| Weight | 5.00 |
| Condition | Refurbished |
Product Description |
|---|
The TPM/FW3.19 module provides a hardware-based security foundation for Asus system boards. It is commonly used in desktops and workstations requiring trusted computing capabilities, especially where data protection and platform integrity are critical. Built for IT professionals and security-conscious users, this TPM module helps to securely generate, store, and manage cryptographic keys, making it an essential component in systems handling sensitive information. Key Features
This module is often found in business and enterprise setups where secure boot and data encryption are necessary. It helps maintain trust in the hardware environment, reducing risks from unauthorized access. By adding TPM/FW3.19 to compatible Asus systems, users get a practical layer of defense that supports modern security measures without affecting everyday performance. |
Use Cases |
|---|
The TPM/FW3.19 module is primarily used in IT environments requiring enhanced hardware-level security integrated with Asus motherboards. It is ideal for enterprise systems, secure workstations, and specialized computing setups where system integrity and cryptographic verification are critical. How It's Used:
By embedding hardware-level security functions, this TPM module helps maintain operational reliability and trust across diverse computing platforms. Its integration with Asus motherboards allows scalable deployment in complex IT infrastructures without sacrificing performance or manageability. |
 Shipping Options
 International Delivery
Requires a UPS, FedEx, or DHL account. Customers may arrange pickup from our US warehouse.
 Payment Methods
We accept Visa, Mastercard, AMEX, Discover, and Wire Transfer.
 Purchase Orders
We process purchase orders for government agencies, enterprises, data centers, and SMBs.