
Subscribe To Our Newsletter!
Subscribe to the newsletter to stay up to date with the latest news and most useful
Newsletter
↑
Back to Top



Product Overview |
|---|
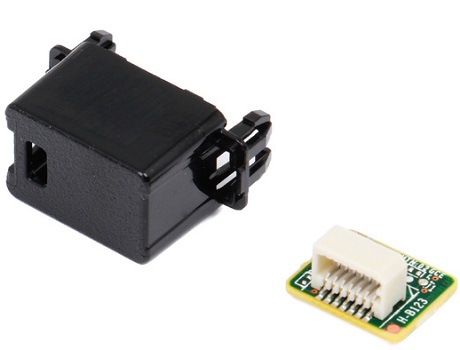
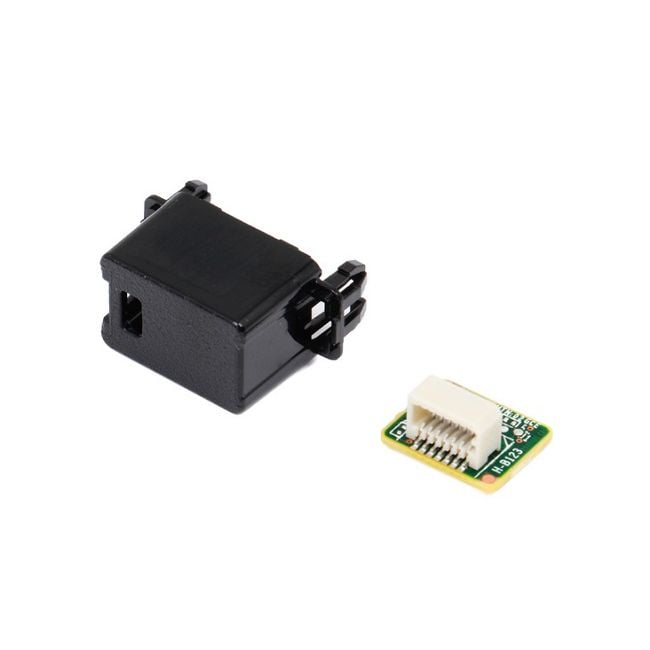
The HPE Trusted Platform Module 2.0 G10 option adds a dedicated security chip that helps servers verify their integrity at startup and store encryption keys safely. It fits into HPE Gen10 servers to support secure boot functions and prevent unauthorized firmware changes, making it a practical security enhancement for enterprise-grade systems. |
General Information |
|
|---|---|
| Brand | HPE |
| Part Number | P31644-001 |
Technical Information |
|
|---|---|
| TPM Version | TPM 2.0 |
| Compatibility | HPE ProLiant Gen10 servers |
Physical Characteristics |
|
|---|---|
| Weight | 5.00 |
| Condition | Refurbished |
Product Description |
|---|
The HPE Trusted Platform Module 2.0 Option is designed to deliver hardware-based security to HPE Gen10 servers. It plays a crucial role in protecting sensitive information by securely storing cryptographic keys and enabling platform integrity checks. Often integrated in enterprise server environments, this TPM module helps ensure that the system boots with trusted software and firmware. IT administrators and security professionals typically deploy this module to strengthen their servers against unauthorized access and firmware tampering. Key Features
This TPM module is commonly found in data centers where security is critical, such as financial institutions, healthcare, and government IT setups. It plays an important role in maintaining system trustworthiness without impacting server performance. |
Use Cases |
|---|
The HPE Trusted Platform Module 2.0 G10 is primarily used in enterprise data centers and secure IT environments where platform integrity and hardware-based security are critical. It is well-suited for organizations deploying HPE Gen10 servers that require enhanced protection for cryptographic keys and secure boot processes to defend against firmware tampering. How It's Used:
Integrating the TPM module into Gen10 servers helps maintain operational reliability by ensuring only authorized firmware and software run, thereby reducing risk in complex IT environments. This hardware-based trust foundation facilitates scalability and secure management in diverse enterprise workloads. |
 Shipping Options
 International Delivery
Requires a UPS, FedEx, or DHL account. Customers may arrange pickup from our US warehouse.
 Payment Methods
We accept Visa, Mastercard, AMEX, Discover, and Wire Transfer.
 Purchase Orders
We process purchase orders for government agencies, enterprises, data centers, and SMBs.