
Subscribe To Our Newsletter!
Subscribe to the newsletter to stay up to date with the latest news and most useful
Newsletter
↑
Back to Top



Product Overview |
|---|
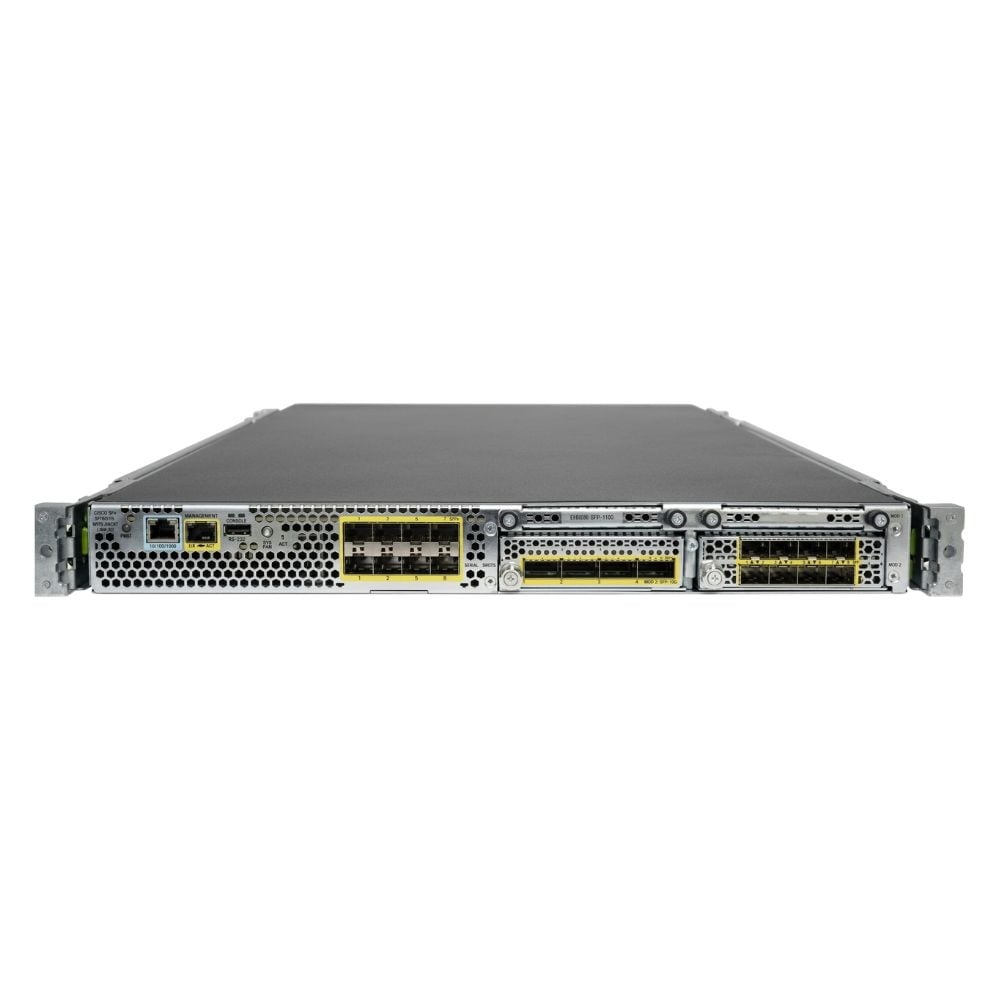
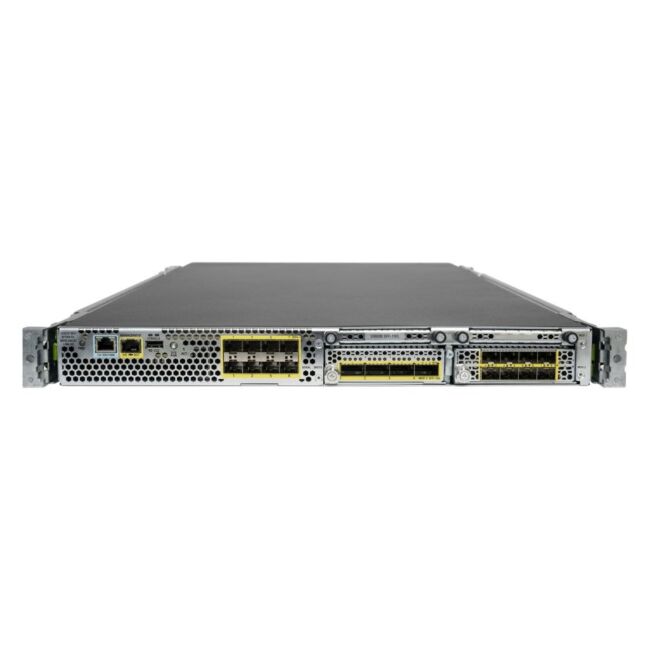
The Cisco Firepower 4140 NGIPS appliance is a 1U rack-mount device built to deliver next-generation intrusion prevention system functionality. It includes two network modules to accommodate flexible connectivity and is tailored to support Cisco's NGIPS application for advanced network security enforcement. |
General Information |
|
|---|---|
| Brand | Cisco |
| Part Number | FPR4140-NGIPS-K9 |
Technical Information |
|
|---|---|
| Interface | Ethernet |
| Ports | 2 (network module slots) |
| Expansion Slots | 2 (network module slots) |
Physical Characteristics |
|
|---|---|
| Form Factor | 1U rack-mount |
| Weight | 3.00 |
| Condition | Refurbished |
Miscellaneous |
|
|---|---|
| Assembly Required | No |
Product Description |
|---|
The Cisco Firepower 4140 NGIPS appliance is a network security device designed to deliver next-generation intrusion prevention capabilities. It is typically deployed in data centers or enterprise networks to monitor, detect, and prevent network threats in real time. Network security professionals and IT teams use this appliance to enhance their defense infrastructure against sophisticated cyber attacks and to enforce security policies across network traffic. Key Features
This appliance serves as a dedicated platform for advanced threat detection and prevention, helping organizations maintain network integrity and security. It integrates into existing infrastructures to provide enhanced visibility and control over network traffic. |
Use Cases |
|---|
The Cisco Firepower 4140 NGIPS appliance is commonly used in enterprise and data center environments requiring robust intrusion prevention capabilities. It benefits organizations needing to monitor and control network traffic to protect against evolving cyber threats. How It's Used:
This appliance plays a critical operational role by providing dedicated hardware to perform deep packet inspection and threat mitigation, allowing security teams to maintain control over network safety and policy enforcement. |
FAQ's |
|---|
|
 Shipping Options
 International Delivery
Requires a UPS, FedEx, or DHL account. Customers may arrange pickup from our US warehouse.
 Payment Methods
We accept Visa, Mastercard, AMEX, Discover, and Wire Transfer.
 Purchase Orders
We process purchase orders for government agencies, enterprises, data centers, and SMBs.