
Subscribe To Our Newsletter!
Subscribe to the newsletter to stay up to date with the latest news and most useful
Newsletter
↑
Back to Top



Product Overview |
|---|
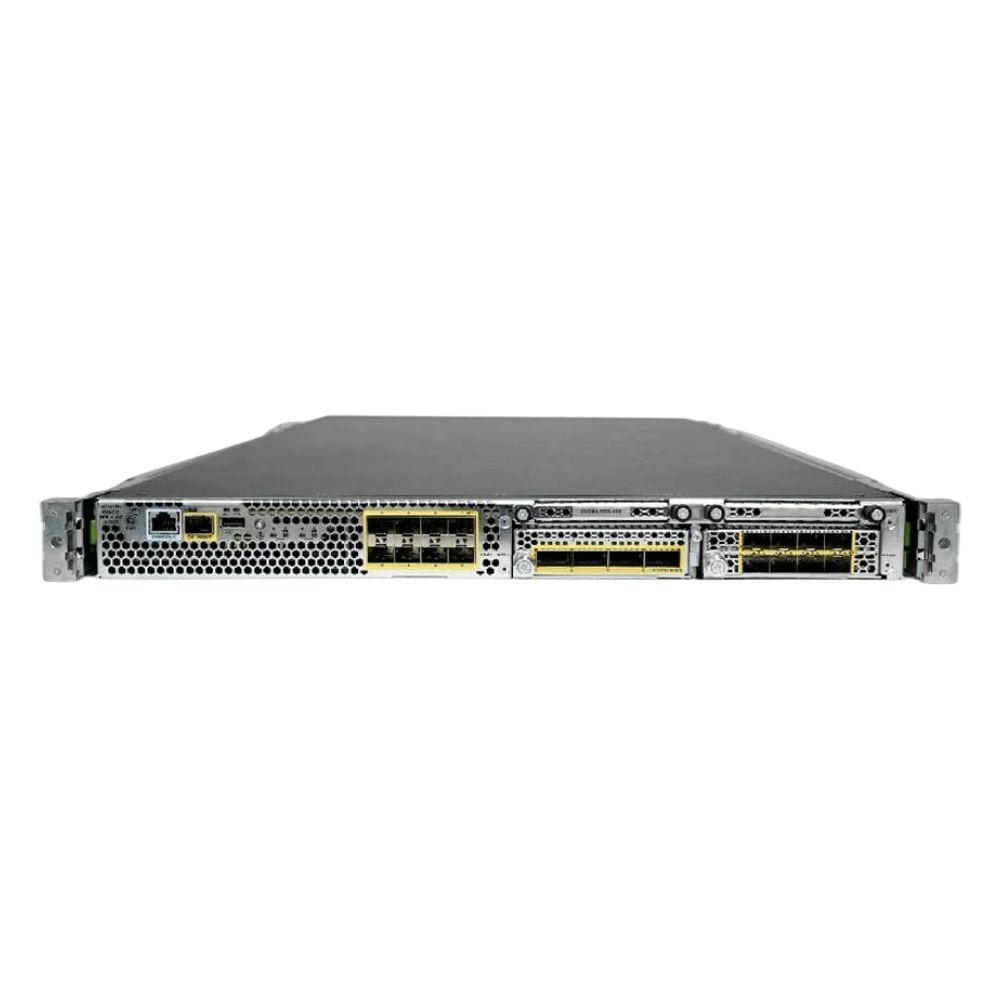
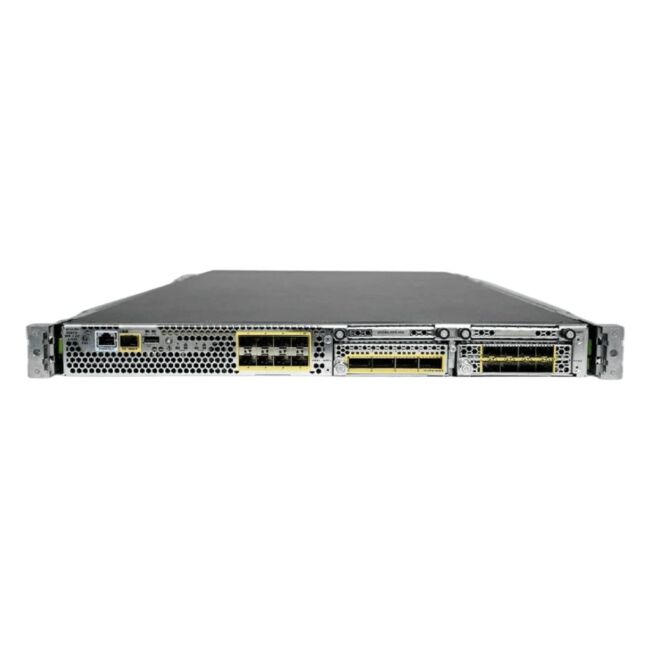
The Cisco Firepower 4140 NGFW appliance is a modular 1U next-generation firewall designed for enterprise network environments. It incorporates two network modules for flexible connectivity and delivers advanced firewall capabilities aligned with Cisco's Firepower architecture. |
General Information |
|
|---|---|
| Brand | Cisco |
| Part Number | FPR4140-NGFW-K9 |
Technical Information |
|
|---|---|
| Interface | Ethernet |
| Ports | 2 |
| Security | Yes |
| VPN Support | Yes |
| OS Support | Cisco Firepower Threat Defense |
Physical Characteristics |
|
|---|---|
| Form Factor | 1U |
| Weight | 3.00 |
| Condition | Refurbished |
Miscellaneous |
|
|---|---|
| Assembly Required | No |
| Eco Friendly | Yes |
| Compliance Standards | WEEE, RoHS, cURus, CE, FCC, CCC, UL, TUV, cULus, CSA, cUL |
Product Description |
|---|
The Cisco Firepower 4140 NGFW appliance is a 1U rack-mount device designed to provide next-generation firewall capabilities. It integrates with Cisco's Firepower security architecture to offer advanced threat protection and network traffic inspection. This appliance is commonly deployed in enterprise data centers or large network environments requiring scalable security solutions. Typically used by network security professionals and IT teams, the Firepower 4140 helps enforce security policies while managing high volumes of network traffic. Key Features
This appliance serves as a core component in network security infrastructure, enabling organizations to establish robust perimeter defenses. Its modular network interfaces allow adaptation to various deployment scenarios. The Firepower 4140 NGFW appliance supports network teams in maintaining secure, inspected, and controlled network access. |
Use Cases |
|---|
The Cisco Firepower 4140 NGFW is typically deployed in data centers and large enterprise networks where high-capacity, adaptable firewall solutions are required. It is suited for IT teams managing complex security policies and network traffic inspection. How It's Used:
Overall, this appliance plays a vital role in establishing controlled and secure network boundaries. It assists administrators in managing and inspecting network flows while adapting to specific infrastructure requirements. |
FAQ's |
|---|
|
 Shipping Options
 International Delivery
Requires a UPS, FedEx, or DHL account. Customers may arrange pickup from our US warehouse.
 Payment Methods
We accept Visa, Mastercard, AMEX, Discover, and Wire Transfer.
 Purchase Orders
We process purchase orders for government agencies, enterprises, data centers, and SMBs.