
Subscribe To Our Newsletter!
Subscribe to the newsletter to stay up to date with the latest news and most useful
Newsletter
↑
Back to Top



Product Overview |
|---|
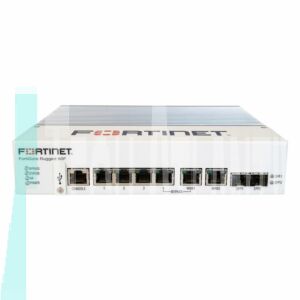
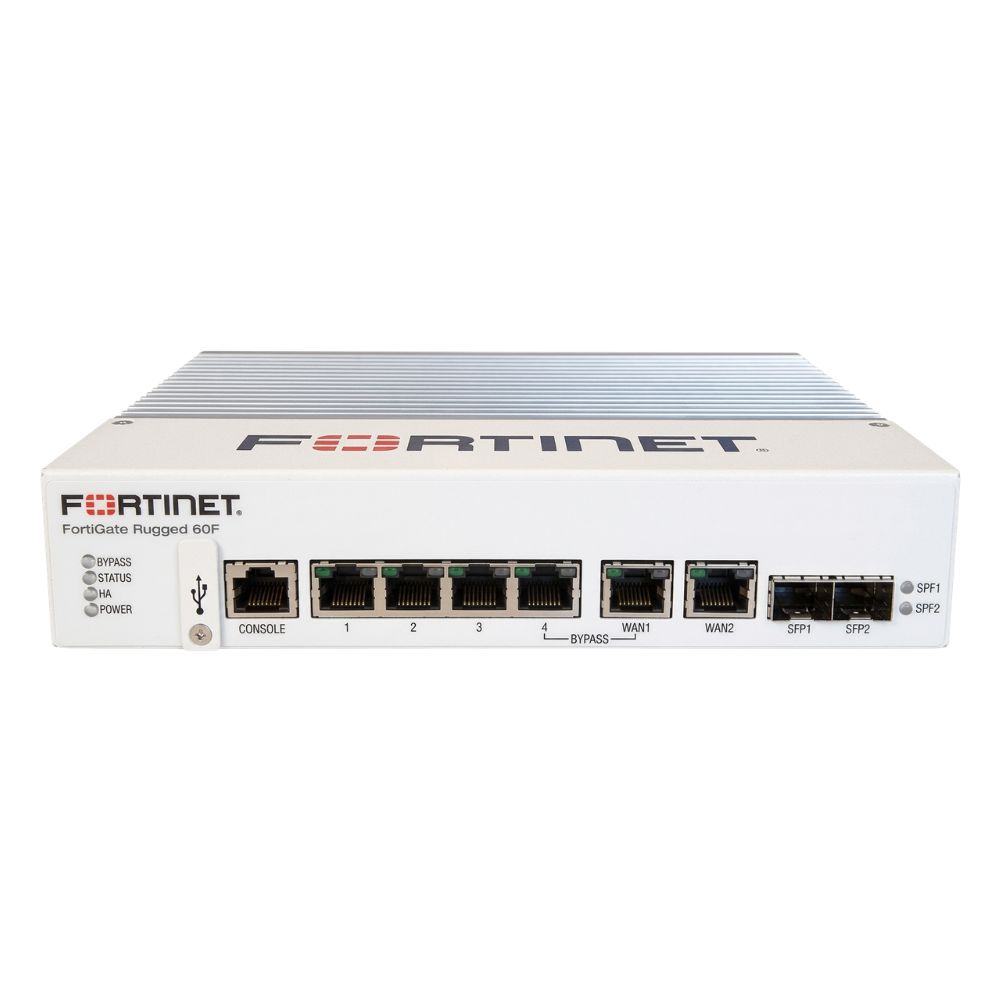
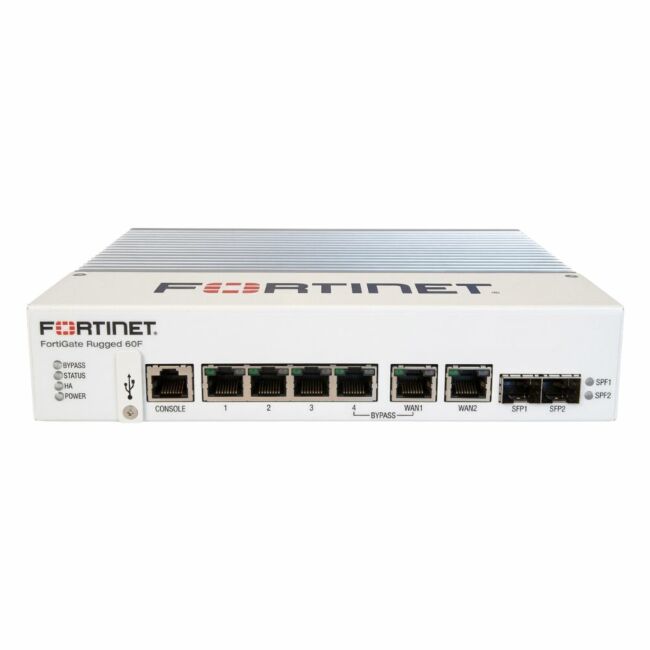
The FortiGate FGR-60F is a network security appliance equipped with 4 RJ-45 Ethernet ports and 2 SFP ports, designed to implement firewall protection and traffic management. It includes a bypass setup configured between WAN1 and Port 4 to support continuity of network operations during maintenance or failure events. |
General Information |
|
|---|---|
| Brand | Fortinet |
Technical Information |
|
|---|---|
| Interface | RJ-45,SFP |
| Ports | 4 x RJ-45,2 x SFP |
| Security | Yes |
| VPN Support | Yes |
Physical Characteristics |
|
|---|---|
| Form Factor | Desktop |
| Weight | 3.00 |
| Condition | Refurbished |
Miscellaneous |
|
|---|---|
| Assembly Required | No |
| Compliance Standards | RoHS, CE, FCC, UL |
Product Description |
|---|
The Fortinet FortiGate FGR-60F is a security appliance engineered to provide network firewall and traffic control functionalities. It features four RJ-45 Ethernet ports alongside two SFP ports, allowing flexible connectivity options. The device includes a bypass setup specifically arranged between WAN1 and port 4 to maintain traffic flow in case of device failure or maintenance. This appliance is generally deployed in network environments requiring robust firewall protection and traffic management, commonly used by IT security teams and network administrators to safeguard enterprise systems. Key Features
The FGR-60F performs a critical role in enforcing security policies and managing data traffic within a network. Its bypass feature helps ensure uninterrupted connectivity, and its combination of RJ-45 and SFP ports provides adaptability to different infrastructure needs. |
Use Cases |
|---|
The FortiGate FGR-60F is typically used in enterprise or branch office network environments where firewall protection and controlled traffic management are required. It is suited for organizations looking to maintain continuous network operation with flexible connectivity options. How It's Used:
Overall, this appliance is deployed to ensure secure and manageable network traffic flow while minimizing service interruptions through its bypass feature and multi-port design. |
FAQ's |
|---|
|
 Shipping Options
 International Delivery
Requires a UPS, FedEx, or DHL account. Customers may arrange pickup from our US warehouse.
 Payment Methods
We accept Visa, Mastercard, AMEX, Discover, and Wire Transfer.
 Purchase Orders
We process purchase orders for government agencies, enterprises, data centers, and SMBs.